Company workspaces
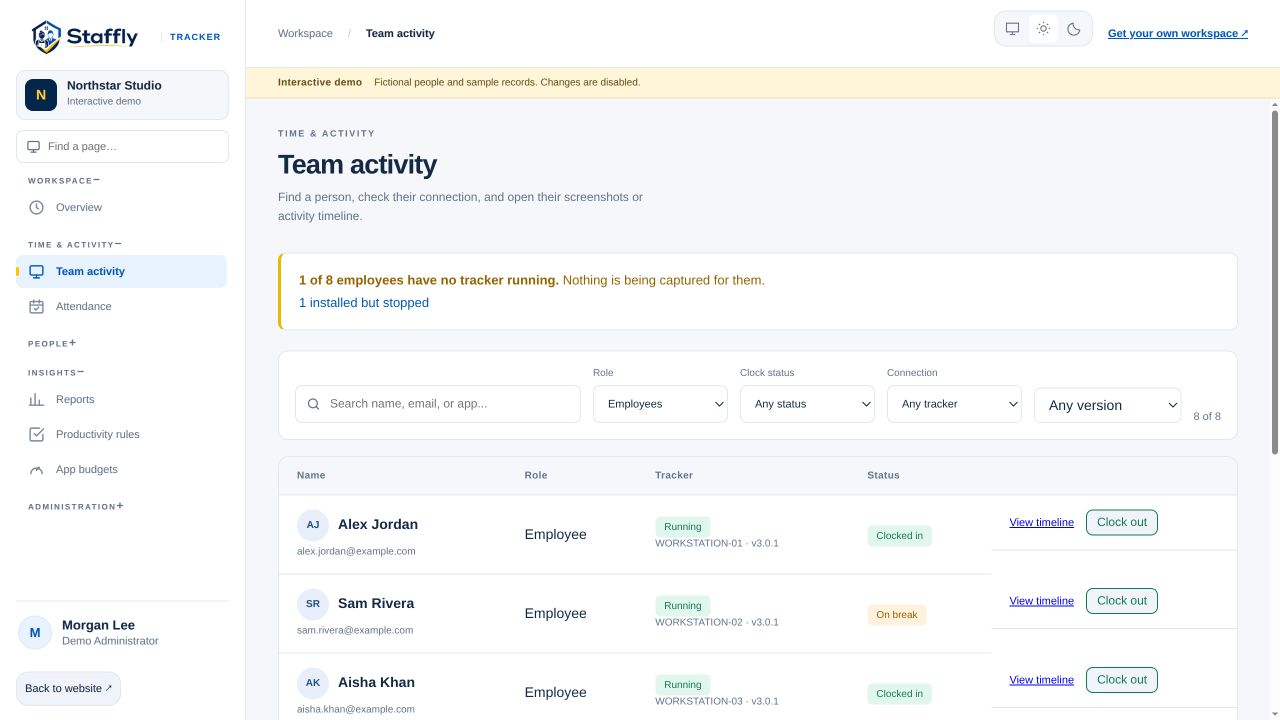
Commercial companies operate in separate tenant workspaces. Company users sign in through their workspace; the platform owner console manages tenant access separately.
STAFFLYTRACKER GUIDE
Understand the separation between company workspaces, role-based access, screenshot retention and your organisation’s tracking policy.
Commercial companies operate in separate tenant workspaces. Company users sign in through their workspace; the platform owner console manages tenant access separately.
Use administrator and manager accounts for the work they are authorised to perform. Review access when responsibilities change. Sharing passwords weakens accountability and should not be part of your rollout.
Configure the retention period according to your policy. Verify that it matches your needs before collecting images, and understand that deleting live records and expiring backups are separate operations.
Screenshots may capture whatever is visible during permitted capture. Do not assume automatic patient-data removal, universal redaction or a compliance certification. Discuss your exact requirements before enabling the workflow.
Public StafflyTracker domains use HTTPS. Device security, account protection and your organisation’s handling of exports remain part of the overall process.
Confirm hosting, backup expectations, retention, permitted administrator access and contractual requirements in writing. This page describes product handling; it is not a claim of SOC 2, ISO 27001 or healthcare certification.
LET’S MAKE WORK A LITTLE CLEARER
Show us how your team works. We’ll show you where StafflyTracker fits.